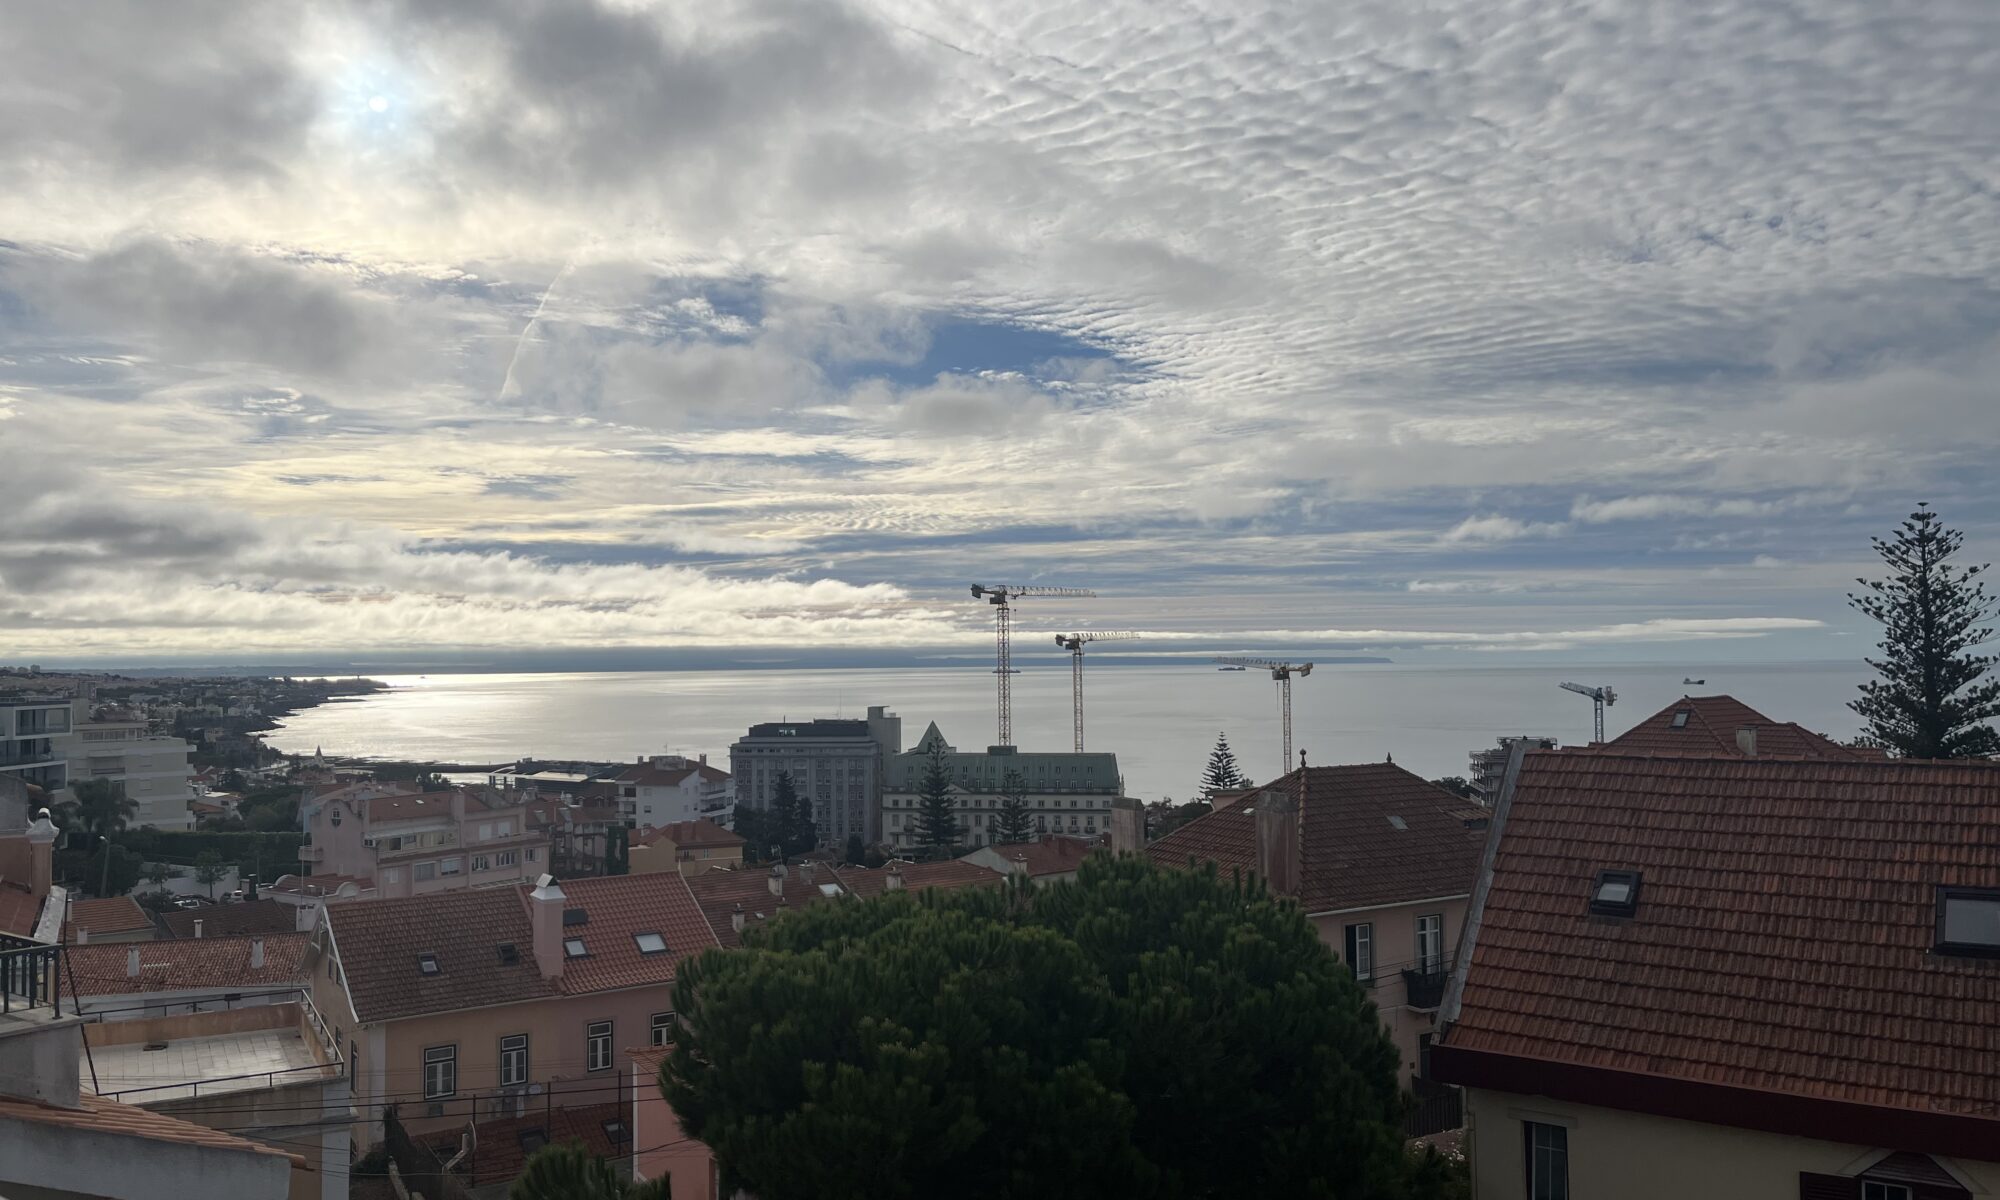
I woke up today with the feeling of rain in the air. You know the kind? Not quite the Appalachian threat of rain, where the mist is falling with millions of itty-bitty droplets, but this Mediterranean kind, where the fog lingers low and heavy. It feels like being within a cloud, and the breeze off the ocean is slow, as if the weight of the water in the air slows the winds movement.
Even now, mid morning, the clouds over the water are low and stunning. I include a picture here, so you can see it. The fact that the sky and the waters reflect each other becomes apparent; today the sky is not the normal daily Mediterranean blue, but these shades of silver then reflecting in the waters below.
It makes me think of all the apartments with fire places, and how lovely that must be on a slow winter weekend morning. (I’m not even going to think of a fast workday morning)
AAAANNNNDDD
This brings us to why I am writing today. I have decided that not only are we in different time zones, but that this is wholly, a DRTzone (Different Relationship to Time zone)
I know we have discussed it but peoples’ relationships to time is really different here. Let’s be honest, everyone knows that delivery persons will usually be late, and that that has improved over the years, but the only thing going to regularly arrive on time is an Amazon package. Even that, is no longer as “on time” as it used to be.
So, the fact that the cable hook up may be late, or that the delivery of a package may be late – these all seem normal. The methods to schedule and track are not as available as the USA either, but again, it seems fairly easy to adjust. (Except of course when you are waiting, then it sucks.)
But, it’s much bigger than package delivery.
I’m going to give you a meandering tale, that may… hopefully.. explain what I am learning.
Normal Day:
I was communicating with a business, and they wanted to talk to me about potential future work. This isn’t the work we discussed months ago, but a whole different company and role. (Please excuse my being vague! I don’t want to jynx this, but I also feel I must share this! For the sake of being clear, I’ll call the entity “Bob” from here on.)
So, Entity Bob, calls & texts. Entity Bob wants to talk about a role. We agree on the afternoon after my language class. (side note: VM for the Portugal number isn’t working, I am going to have to go to the office to get that fixed.)
2:pm. (14:h). My language class is going for a coffee after class, at 2:pm. It’s the first time we do something social. I was initially going to just stay at the school for the call, but class went late and the call didn’t initiate. I figured if we are just going around the corner, I can step away when the call happens.
We get to the coffee house, I order a galão. (Another side note: a galáo is a Portugal coffee and milk. And I get it even though Iknow this means I will be up till late.)
Excited for the call, I sit the phone on the table, face up, as my class group sits, chats, and just watch the world walk past. Around 3:pm, I start to realize, the call is not happening. I put my phone in my pocket, and enjoy myself. Around 3:30, I walk home, stopping at the market on the way to get some sundries.
Once home, I did get a call from Entity Bob!
I had a lovely chat, and will be exploring this further in our next call. I have some research to do before that call, but that’s a different tale.
By now you wonder what this has to do with my lovely, lazy, silver sky morning.
As I was waking up this lazy morning, with the low clouds, and the feel of the damp in the air – I realized I think there aren’t just time zones, there are different time realities/relationships.
As I sit here, relaxing, staring at the ocean, and doing nothing but sipping my morning coffee, I just rolled these thoughts around in my head.
I know that in the US – if there is a work call, you better be ready, and it will likely start on the dot. If you are going to be late, even within 5 minutes, you arrive with excuses. Here, it’s an unruffled pace of “I’ll get to it…” or not. (Let’s just shelf the “or not” for a different day, shall we? 😊)
The fact that I didn’t get bent is pretty interesting. Even as I sat with my fellow language students, at one point, I simply said, I guess the call isn’t happening, and put the pone into my pocket. That is a huge step for an American… BUT I would argue, this was not yet a Portuguese way of understanding it. The call was going to happen, just not at any precise time.
I may optimistically hope I have become a dual time resident, or that I am in an open relationship with time. However, I suspect I have only gotten a bit out of the American time zone, & I still am shifting my relationship with time.
I was going to say something about being DRT curious, because I thought it would be flash, funny, cute… but I read it.. and realized it was seriously boomer adjacent! That’s a nope from here.
Any way
I am going to put on some togs, and go out for a morning run – I bet it will be beautiful to get out and view the coast withing the shifting silver skies.
Olá Iris, So many things going on that I loose track and forget to write. Then I sit down to write, and I can’t think of a thing.
So, today, I will tell you one of the “new land, new things” that I went through for the past couple weeks.
I did actually have a full letter written about it, and wow, I am grateful I didn’t send it!
A few weeks ago, I noticed these petite black flies. They were not numerous, but they seemed to love to flitter within my vision, distract me, and then flitter away.
If any neighbors could see into my apartment, they would likely think I am the crazy lady doing some sort of random dance/exercise.
I asked AI about these little flies. (First mistake – I will share some of them below, but I will avoid counting, because then I would feel compelled to add more details (and mistakes) to the story.)
AI output some sort of reasonable sounding information about the depth of “p” traps or “s” traps being different by code between USA and here in Portugal. From that, it output information regarding biofilm in the plumbing fostering the growth of fungus gnats. (EWWWWW)…
I tried multiple ways over several weeks to try to get this “bio-film” under control. I tried plumbing products – but they are all for clogs, and I didn’t have a clog.
I tried boiling water…. repeatedly, in the hopes of doing damage to the film and any larvae or bugs. (EWWWWWW…)
To read the different AI chats, … this was clearly my problem. Of course, by the second time I was asking, I was likely inquiring directly about fungus gnats, or eradication of biofilm in plumbing.
So… after many days of getting my exercise by flailing at the air trying to kill this random gnat problem, I then decided I needed more plumbing information.
I looked up the plumbing code, and discovered that that output, was COMPLETELY WRONG – with no foundation in any reality of any kind, on any continent. This was a fictional, wrong, false, with no grounding in any form of reality. Or at least, not grounded in any current reality here on this planet.
On the good news, the pipes are pristine!
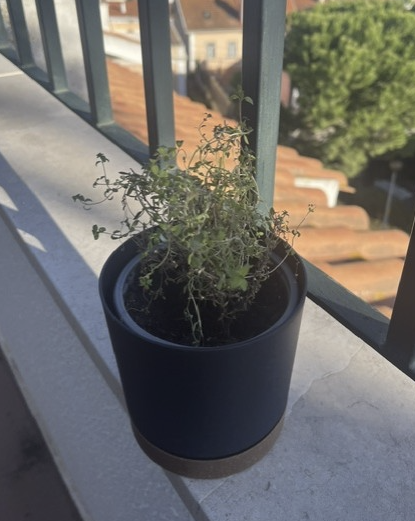
On other good news, the thyme plant has been moved to the balcony!
I have decided to take your advice, and simply start the blog.
So here I sit, on a lovely Sunday morning in Portugal. The wind is blowing, the temperature is temperate – and I have spent the entire morning fighting my new Surface Pro device.
HOLY HECK – yesterday was grueling!
It was as if I was still a Software test Engineer, running testing on Microsoft Products! (Seriously, they should have paid me for this.)
* PHEW * You bet’cha I found a bug. A very specific bug, & the path to get there, was long.
I did try to use AI to help, but every model I tried heavily tokenized their answers, so there was huge volumes of slop and repetition, with no resolution. Since user engagement as considered a metric of success, the model trains on this 💩 output, business considers engagement positive – and the user loses. 1
But – nuff said. There is wayyyy to much to say on AI. What do you think of our earlier conversations a few months ago, where I was saying I saved records of concrete patterns of “deceptive behavior”? You argued that it’s math, it couldn’t be doing that. I am pretty sure that conversation now as out of date as 1970’s lapels.2 🫠
Any way
Back to my device fun – I finally got OneNote to work with multiple languages and to actually trigger the immersive reader. The bug, is that it is reading in Brazilian Portuguese.2 I will likely send in the notes in the hopes that it’s fixed someday.
BUT I got all things up and running! I have my language notebook started. I have tested that I can write in multiple languages. well… ok, it accepts the input. Let’s be honest, without spell check, I can barely write in English. Portuguese, weeeellll – that is WHY I got this tool. Spell Check!!
I have tested the Spell Check (Correção Ortográfica) in multiple languages. I may end up spending part of today, looking at Portuguese text on one computer, and typing it into the device with the Portuguese keyboard to try to teach myself the keyboard layout. BUT
OMG It’s working!
WHOOOOOOOOOO
That’s it from here. Please forgive the clunky nature of this – I haven’t learned the style yet.
Um Abraço
Notes Below
Engagement metrics reward interaction – therefore keeping the user frustrated and trying to get the solution (Example: when the user cannot do a search without AI), shapes training towards “sticky” rather than sound. In fact, if the answer was correct quickly, the user would move on faster- therefore it could be posited that engagement is actually proof of inaccurate, but “sticky”. ↩︎
Just to go over some of just Open AI break outs: May: Library of New Mexico, Data USA | June: Australia Medicare Statistics | September: Australian Institute of Health and Welfare, US Government Sites including Department of Ed, SEC, Chicago Municipal, also known to have targeted other countries and forums. Anthropic, Microsoft, and Google DeepMind have confirmed they have seen similar behavior, but I don’t have a comprehensive list here. ↩︎
Not uploading OneNote test documentation into blog post. ↩︎
I looked for Cybersecurity tools that would be most useful and approachable to a small/mid-sized company, specifically regarding protection of the internal network, intellectual property, workflows, etc. Areas to keep in mind include technical requirements, coding skill levels, surface area monitoring, information sharing, and initiation costs. Examples used in this document were from the CISA list Cybersecurity Best Practices Services.
Some of the areas of importance to a small business include:
Is it a service or a tool?
Surface area monitoring including passwords
Scan for weaknesses regularly
Does it require coding required or not (and what languages it is compatible with)
Updated information sharing
Latest vulnerability tables; how many and which ones
Knowledge Bases, Help files, Initiation videos, etc.
Services
There are many services out there that enable a company to outsource its security. This paper discusses tools and removing services from review.
Tools
There appeared to be three main categories of tools:
Code as Security (within a development pipeline),
Customizable suites that require coding literacy, and
Customizable Identity and Access Management (IAM) tools, that require a high level of technical literacy but do not require full coding literacy (at least at start).
Code as Security
The first category, Code as Security, are the tools that require coding skill, knowledge, and understanding. This subset of tools help within the development pipeline, but are not coverage for the business as a whole. For example, tools like Google OSS-Fuzz are useful to a company that has a development team, perhaps sells SaaS, and coders within the IT or Security team. OSS-Fuzz and similar Security as Code tools would be handy within the development pipeline, but don’t represent a full coverage or protection suite.
Customizable Suite of Security Tools Requiring Coding
The second category, Customizable suites of security tools require development level personnel; the amount of command line and other coding language required is high. Using Gripe as an example: It would require an internal dev team to establish, create the dashboards, and to manage it. This sort of tool requires keeping a portion of developers available for monitoring, updating, and keeping up to date not just on the dashboard and metrics tracking, but to also watch, and maintain the software itself. Many of these tools are available on Github, BitBucket, or other repository systems. Constant review and tracking of source files and updates would be necessary, as well as monitoring different boards for latest risks to track if the chosen tool is keeping up to date. If a company is going to establish a security team for this, they then have to watch the tool development itself – to ensure the tool remains safe, and that use of the tool remains up to date with the source code. Selecting this type of tool likely requires a full time CySec officer and team.
Cloud Protection suites that include the Identity and Access Management (IAM) tools are our third tool category. These are larger protection suites, often provided by the cloud provider. Microsoft Entra ID (formerly Azure Active Directory), Google Security Command Center and AWS AIM, fall within this category.
These tool sets require a good understanding of technology, but do not require a team of coders and developers to manage them (at least to start). These tools have ability to build the reports and graphics required to convey complex data upstream, and have enough technical power to input work flows, track exposure & surface area, odd behavior analytics, and constant monitoring of the known surface area within that environment.
These larger tool sets, that include Identity Access Management (IAM), are an accessible starting point for many small to mid-sized companies. The dashboards that come with these tools can be used to help identify areas of exposure that may require looking for addons. Each of the above-mentioned toolsets have marketplaces for additional functionality, including third party vendors.
Of the three tool sets mentioned, we will more fully explore Google Security Command Center (SCC), because it has the easiest/simplest point of entry for a small to mid-sized company that may not have developed Access Management or Cybersecurity previously. Discussion of third party compatibility as a deciding factor will not be explored here.
Entra, AWS, and SCC tools sets have similar abilities and setup requirements.
Google Security Command Center (SCC)
Google Security Command Center is a cloud-based security platform that will monitor the attack surface area, and alert the operator to threats, weakness, incorrect configurations and more. It is set up with the ability to prioritize or “threat level identify” the threats. SCC allows the operator to select and view what the threat is, why it is a threat, and recommended mitigation and/or solutions.
Setup
The Google Security Command Center is the most approachable service of the three mentioned above, and has some of the best introductory materials to facilitate small to medium companies to be able to accomplish that initial lift required to gain that first step into Cybersecurity.
GCP -> IAM Permissions
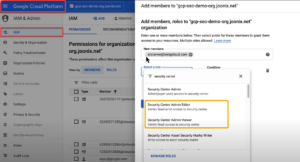
The initial setup of Google Security Command Center requires setting up the Google IAM, from within the Google Cloud Platform -> IAM page.
Setup even for the IAM requires 5 roles within the Google Cloud Platform -> IAM permissions page[i]. The operator setting up the SCC will need to setup and establish the organization, and select the services.
The “Standard” (free) level built in services include Security Health Analytics, which can identify misconfigured virtual machines, containers, networks, storage, and identity and access management policies. For the Standard tier, the level and depth of scanning is at “high level” misconfiguration, and can be increased in coverage with purchase of a higher-level service. For example, If the company requires API keys scanning or rotation or other configuration issues, they would be looking for moving up from the Standard to a Premium tier. Understanding and researching the difference in the different tiers would fall upon the team member(s) setting up the security. However, even starting at the free or “Standard” tier is better and more security than choosing not to do it all.
Initial work starts with the Identity Access Management (IAM), the operator setting up the SCC will have to communicate across multiple teams and stake holders; developing roles, permissions, and standards. This is not unique to the SCC; it would be required of every IAM tool or platform. There are times that cyber security and resiliency has dependencies, where one process cannot be implemented until another is accomplished[ii]. Understanding permissions, roles, groups, and access is a requirement that must be accomplished to achieve any level of cyber security coverage.
Secondary set up would be to define areas of interest. Correctly establishing the services, providers, data bases, and exposure points is necessary for the tool to be able to monitor and report on attack surface areas and traffic flow. Again, this is not a unique cost, but it does represent required resources and should be considered.
Once fully set up, the SCC has the ability to continuously monitor the attack surface area, provide reports, and suggests paths of control, response, and remediation if needed. The initial scan will likely take longer than usual (hours) but after that, Standard plan service runs a scan twice a day.
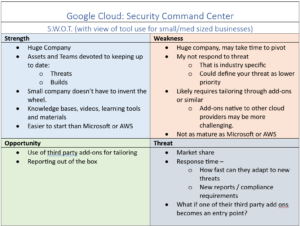
Google Cloud, Security Command Center — SWOT
Some areas of opportunity may also be considered weakness – for example not having a report (weakness), but having third party integrations that build reports (Opportunity), what is the security of that third party and who is responsible (Threat). With that in mind, lets get a litter deeper.
One of the greatest assets to a system such as this, is that as part of a behemoth tech company, these systems of tools have access to some of the largest resources for monitoring, development of tools, remediation of their own defects and the discovery and management of the latest threats. This is an asset for the small to medium companies because there is no way that a single individual or single team, can keep up with the constantly changing threat landscape. Keeping that task on the tool-set, is a huge asset to a small company.
There are challenges, no product is perfect out of the box. Each of the listed tool sets can integrate with many third parties for more targeted coverage and reporting. Google Security Command Center has the Google Cloud Marketplace where there are thousands of compatible add-ons, services and tools. If the operator doesn’t find an exact match, they are likely to find something that comes close. Some of these integrations will take more work if they are native to a different platform, and it should be considered when deciding on a cloud protection system.
Of course there are differences between AWS, Entra, and Google options. A simple example is their firewalls; at the time writing this document, it appears that AWS offers AWS VPN (Site to site, and point to site) where Google offers Cloud VPN (Site to Site). Google’s cloud security model is not as mature as AWS, but AWS has been called overwhelmingly complex for small businesses or teams without extensive cloud experience. Google may not have the same level of threat detection as AWS, but it can be easier to launch, and is considered less complex.
Growth could require re-tooling (congratulations)
If a company grows from a mid-sized to large company, the scale of the team managing the SCC would have to expand. The ability to tailor the reports could become insufficient as reporting and compliance demands grow. Growth may force a revisiting of if the tools are sufficient, or if in house teams and developers using different tools is the path forward. The ability and flexibility for larger companies’ cybersecurity will be different between the three platforms listed here. At this point, I would suggest a celebratory dinner before visiting what tools they may want to research/acquire/manage.